
|
|
|
|
|
 |
 |
|
|||||||
 أهلا وسهلا بكـ يا غير مسجل |
||
|
منتديات الأمل على الفيسبوك
|
باب التسجيل مغلق حاليا في منتديات الأمل
|
منتديات الأمل على تويتر
|
|
تابع منتديات الأمل | |
| قسم الطلبات وحلول مشاكل الحاسوب إذا ما احتجت أي برنامج، أو شرحا لبرنامج ما، أو صادفك أي مشكل في حاسوبك، فاكتب طلبك هنا ولن تخذل إن شاء الله. |

 |
|
|
أدوات الموضوع | انواع عرض الموضوع |
 11-04-2009, 17:47 |
#11 | ||||
|

أهلا بك أخي العزيز سرحان مجددا.. اقتباس:
فكفى ... أشعر بالخجل من اشغالك أخي الحبيب
بالنسبة لحذف الملفات المستعصية الحذف فهذا البرنامج سيفيدك إن شاء الله، فلتجعله رفيقا لك: برنامج Unlocker أيضا هلا حددت لي أية رسالة لازالت تظهر في منتديات الأمل وهل في متصفح الفايرفوكس أم الإكسبلورر فقط؟ وهل تعذر على HijackThis حذف ذلك المفتاح؟ في الانتظار... مني لك أرق تحية.. التوقيع
|
||||
|
11-04-2009, 19:02
|
#12 | ||||
|
اخي العزيز هادي هذه الكلمات حقا كنت اشعر بها بالخجل والأحراج ولكن كرمك هو المشجع واوعدك إن شاء الله أن لا تسمع مني مثل هذه الكلمات
والآن اكتشفت ان هذه الرسائل في الاكسبلورر وليست في الفاير فوكس 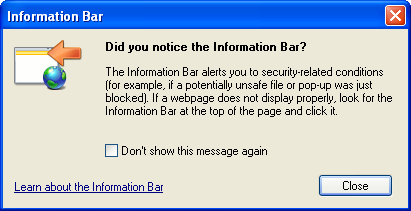  وهذا آخر تقرير بعد حذف SeaPort.exe - على الرغم من انني لا اعرف هذا الملف يخص أي شيء بالضبط؟؟؟ هههه- من الـ C باستخدام UNLOCKER كود:
Logfile of Trend Micro HijackThis v2.0.2
Scan saved at 09:42:54 م, on 11/04/2009
Platform: Windows XP SP3 (WinNT 5.01.2600)
MSIE: Internet Explorer v7.00 (7.00.6000.16791)
Boot mode: Normal

Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Avira\Avira Premium Security Suite\sched.exe
C:\Program Files\Google\Update\GoogleUpdate.exe
C:\WINDOWS\Explorer.EXE
C:\Program Files\Avira\Avira Premium Security Suite\avguard.exe
C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
C:\Program Files\Avira\Avira Premium Security Suite\avesvc.exe
C:\Program Files\Common Files\Real\Update_OB\realsched.exe
C:\Program Files\Bonjour\mDNSResponder.exe
C:\Program Files\Adobe\Reader 8.0\Reader\Reader_sl.exe
C:\Program Files\Unlocker\UnlockerAssistant.exe
C:\Program Files\Common Files\Microsoft Shared\VS7DEBUG\MDM.EXE
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\system32\svchost.exe
C:\Program Files\Yahoo!\SoftwareUpdate\YahooAUService.exe
C:\Program Files\Messenger\msmsgs.exe
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\Internet Download Manager\IDMan.exe
C:\Program Files\Avira\Avira Premium Security Suite\avmailc.exe
C:\Program Files\Avira\Avira Premium Security Suite\AVWEBGRD.EXE
C:\Program Files\Internet Download Manager\IEMonitor.exe
C:\Program Files\Mozilla Firefox\firefox.exe
C:\WINDOWS\system32\wuauclt.exe
C:\Program Files\Trend Micro\HijackThis\HijackThis.exe

R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Bar = http://us.rd.yahoo.com/customize/ie/defaults/sb/msgr9/*http://www.yahoo.com/ext/search/search.html
R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = http://www.yahoo.com
R1 - HKCU\Software\Microsoft\Internet Explorer\SearchURL,(Default) = http://us.rd.yahoo.com/customize/ie/defaults/su/msgr9/*http://www.yahoo.com
R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyOverride = *.local
O2 - BHO: IDM Helper - {0055C089-8582-441B-A0BF-17B458C2A3A8} - C:\Program Files\Internet Download Manager\IDMIECC.dll
O2 - BHO: Skype add-on (mastermind) - {22BF413B-C6D2-4d91-82A9-A0F997BA588C} - C:\Program Files\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O2 - BHO: RealPlayer Download and Record Plugin for Internet Explorer - {3049C3E9-B461-4BC5-8870-4C09146192CA} - C:\Program Files\Real\RealPlayer\rpbrowserrecordplugin.dll
O2 - BHO: Search Helper - {6EBF7485-159F-4bff-A14F-B9E3AAC4465B} - C:\Program Files\Microsoft\Search Enhancement Pack\Search Helper\SearchHelper.dll
O2 - BHO: Windows Live Sign-in Helper - {9030D464-4C02-4ABF-8ECC-5164760863C6} - C:\Program Files\Common Files\Microsoft Shared\Windows Live\WindowsLiveLogin.dll
O4 - HKLM\..\Run: [TkBellExe] "C:\Program Files\Common Files\Real\Update_OB\realsched.exe"  -osboot
O4 - HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 8.0\Reader\Reader_sl.exe"
O4 - HKLM\..\Run: [UnlockerAssistant] "C:\Program Files\Unlocker\UnlockerAssistant.exe"
O4 - HKCU\..\Run: [MSMSGS] "C:\Program Files\Messenger\msmsgs.exe" /background
O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 - HKCU\..\Run: [IDMan] C:\Program Files\Internet Download Manager\IDMan.exe /onboot
O4 - HKUS\S-1-5-18\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'SYSTEM')
O4 - HKUS\S-1-5-18\..\RunOnce: [RunNarrator] Narrator.exe (User 'SYSTEM')
O4 - HKUS\.DEFAULT\..\Run: [CTFMON.EXE] C:\WINDOWS\system32\CTFMON.EXE (User 'Default user')
O4 - HKUS\.DEFAULT\..\RunOnce: [RunNarrator] Narrator.exe (User 'Default user')
O4 - Global Startup: Adobe Gamma Loader.lnk = C:\Program Files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe
O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~1\MICROS~2\Office12\EXCEL.EXE/3000
O8 - Extra context menu item: تحميل الكل بـ إنترنت داونلود مانيجر - C:\Program Files\Internet Download Manager\IEGetAll.htm
O8 - Extra context menu item: تحميل بـ إنترنت داونلود مانيجر - C:\Program Files\Internet Download Manager\IEExt.htm
O8 - Extra context menu item: تحميل محتوى فيديو (إف.إل.في) بـ إنترنت داونلود مانيجر - C:\Program Files\Internet Download Manager\IEGetVL.htm
O9 - Extra button: Blog This - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra 'Tools' menuitem: &Blog This in Windows Live Writer - {219C3416-8CB2-491a-A3C7-D9FCDDC9D600} - C:\Program Files\Windows Live\Writer\WriterBrowserExtension.dll
O9 - Extra button: Skype - {77BF5300-1474-4EC7-9980-D32B190E9B07} - C:\Program Files\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll
O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe
O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe
O16 - DPF: {30528230-99f7-4bb4-88d8-fa1d4f56a2ab} (Installation Support) - C:\Program Files\Yahoo!\Common\Yinsthelper.dll
O16 - DPF: {6E32070A-766D-4EE6-879C-DC1FA91D2FC3} (MUWebControl Class) - http://update.microsoft.com/microsoftupdate/v6/V5Controls/en/x86/client/muweb_site.cab?1232133566187
O16 - DPF: {BFF1950D-B1B4-4AE8-B842-B2CCF06D9A1B} (Zylom Games Player) - http://game02.zylom.com/activex/zylomgamesplayer.cab
O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL
O23 - Service: Avira Premium Security Suite Firewall (AntiVirFirewallService) - Avira GmbH - C:\Program Files\Avira\Avira Premium Security Suite\avfwsvc.exe
O23 - Service: Avira Premium Security Suite MailGuard (AntiVirMailService) - Avira GmbH - C:\Program Files\Avira\Avira Premium Security Suite\avmailc.exe
O23 - Service: Avira Premium Security Suite Scheduler (AntiVirScheduler) - Avira GmbH - C:\Program Files\Avira\Avira Premium Security Suite\sched.exe
O23 - Service: Avira Premium Security Suite Guard (AntiVirService) - Avira GmbH - C:\Program Files\Avira\Avira Premium Security Suite\avguard.exe
O23 - Service: Avira Premium Security Suite WebGuard (antivirwebservice) - Avira GmbH - C:\Program Files\Avira\Avira Premium Security Suite\AVWEBGRD.EXE
O23 - Service: Apple Mobile Device - Apple Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe
O23 - Service: Avira Premium Security Suite MailGuard helper service (AVEService) - Avira GmbH - C:\Program Files\Avira\Avira Premium Security Suite\avesvc.exe
O23 - Service: Bonjour Service - Apple Inc. - C:\Program Files\Bonjour\mDNSResponder.exe
O23 - Service: Google Update Service (gupdate1c992d5c907461a) (gupdate1c992d5c907461a) - Google Inc. - C:\Program Files\Google\Update\GoogleUpdate.exe
O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe
O23 - Service: Cyberlink RichVideo Service(CRVS) (RichVideo) - Unknown owner - C:\Program Files\CyberLink\Shared Files\RichVideo.exe (file missing)
O23 - Service: SeaPort - Unknown owner - C:\Program Files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe (file missing)
O23 - Service: ServiceLayer - Nokia. - C:\Program Files\PC Connectivity Solution\ServiceLayer.exe
O23 - Service: Yahoo! Updater (YahooAUService) - Yahoo! Inc. - C:\Program Files\Yahoo!\SoftwareUpdate\YahooAUService.exe

--
End of file - 8159 bytes
ودمت بكل خير اخي الغالي التوقيع
 |
||||
|
11-04-2009, 19:42
|
#13 | ||||
|
أهلا بك مجددا أخي سرحان.. كود:
O23 - Service: SeaPort - Unknown owner - C:\Program Files\Microsoft\Search Enhancement Pack\SeaPort\SeaPort.exe (file missing) كود:
O23 - Service: Cyberlink RichVideo Service(CRVS) (RichVideo) - Unknown owner - C:\Program Files\CyberLink\Shared Files\RichVideo.exe (file missing) بالنسبة لتلك النافذة التي تظهر في الإنترنت إكسبلورر فأعتقد بأن لها علاقة بالحمايةالتي يوفرها هذا المتصفح، وأعتقد أنها تظهر لك حينما تريد إضافة بعض الأزرار والفواصل، لأن الرسالة متعلقة بالحماية من النوافذ المزعجة، وتخبرك إن كنت تثق في الموقع فقم بالموافقة عليه، ولذلك فأطلب منك القيام بالتالي: حينما تظهر النافذة التالية قم بالتأشير على الخانة ضمن الإطار الأزرق التالي حتى لا تظهر هذه النافذة مجددا: 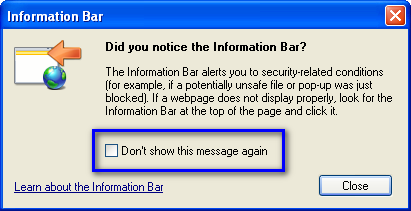 ومن تم وفي ذلك الشريط الذي يظهر في المتصفح اختر السماح للموقع باستعمال النوافذ التي تعمل بالجافا سكربت.. في انتظار النتيجة، مني لك أرق تحية.. التوقيع
|
||||
|
12-04-2009, 14:32
|
#14 | ||||
|
التوقيع
|
||||
|
12-04-2009, 14:44
|
#15 | ||||
|
أهلا بك أخي العزيز سرحان من جديد، وأرجو أن يكون يومك يمر بكل خير وكما تحب إن شاء الله.. التوقيع
|
||||
|
12-04-2009, 20:36
|
#16 | ||||
|
اخي الكريم هادي لك خالص الشكر والتقدير من صميم قلبي
تم تحميل البرنامج وقمت بتنفيذ الشرح الرائع خطوة بخطوة وهو برنامج رائع جدا ولم يأخذ وقت إلا في تنظيف الأقراص العميق أخذ وقت طويل جدا وهذا ما أخرني في الرد تم الاختبار بالـ HijackThis وما زال هذا المفتاح موجود للأسف  وللأسف فقد حذفت هذا البرنامج من وقت تثبيته وليس لدي الخبرة الكافية على safe mode ولكن لا داعي لحذفه أخي الحبيب ما دام هذا المفتاح يحبني بعد كل هذا .. وأظن انه من النوع المسالم فلندعه وشأنه  وبالنسبة للنوافذ فهذه أمثله على النوافذ التي تفتح تلقائيا وهي تفتح مع أي موقع وأنا عادة تصفحي محدود في مواقع معدودة واعتقد ان هذه النوافذ ليست ضارة ولكن كان المراد التحكم بها أو الاستفسار عن لماذا تفتح تلقائيا 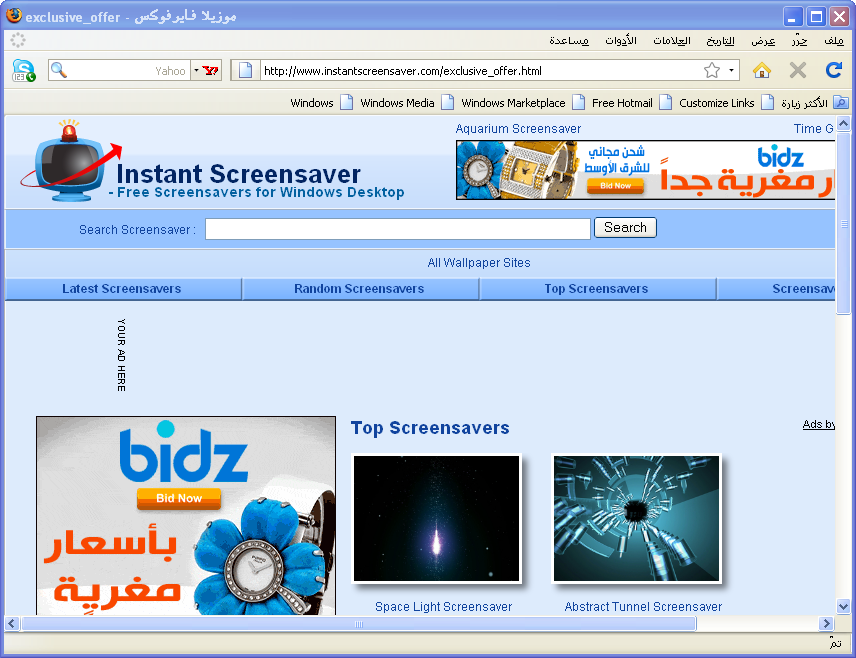 وهذا موقع آخر وهنا أجريت تجربة للدخول فأدخلني لتسجيل دخول للـ facebook وبعد تسجيل الدخول حذرني الـ avira بوجود ملفات ضارة وقمت بحذفها ولم يدخل للـ facebook 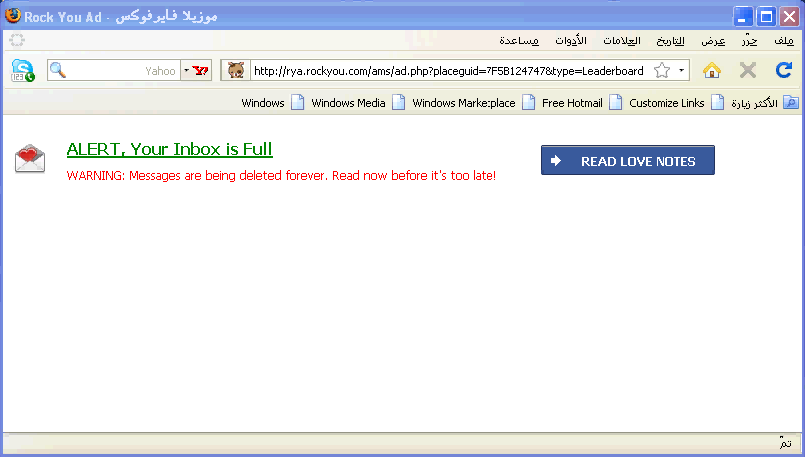 وهذا مرة أخرى ولم افتح سوى منتدانا الأمل 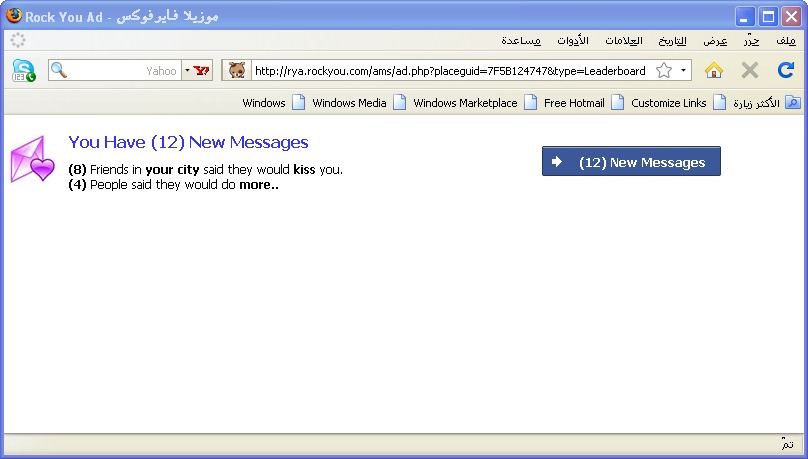 والآن قد تم تثبيت أربعة برامج combofix, HijackThis, Revo Uninstaller and unlocker وعندي برنامج avira الغير الحر وأظن انه اقترب انتهاءه فأريد بديل حر قوي كما أريد منك ختام الموضوع ببعض النصائح للتنسيق بين هذه البرامج أو أشغلها بصفة دورية؟؟ أم ماذا؟ لك جزيل الشكر أخي على مجهودك ومساعدتي في حل مشكلتي وعذرا لو كنت أجهدتك معي وخاصة لنقص خبرتي في هذه المجالات والآن أشعر بأن الحاسوب أصبح نظيفا وأطمننت على سلامة النظام بفضل توجيهاتك دمت اخي كما تحب ودامت الأخوة بيننا التوقيع
|
||||
|
12-04-2009, 21:30
|
#17 | ||||
|
أهلا بك أخي سرحان.. التوقيع
|
||||
|
13-04-2009, 17:57
|
#18 | ||||
|
أخي الحبيب هادي لم أرى ولم أتوقع مثلك في حب خدمة الأخرين
جزاك الله خيرا وبارك الله فيك 1- قمت بحذف الـ avira نهائيا 2- قمت بتثبيت الأفيرا الحر وأعطاني إلى 20/7/1431 هـ وعملت مسح على الوضع الأمن وهذه نتائجه كل شيء على حساب المدير فلا يوجد حساب خاص الآن كود:
Avira AntiVir Personal
Report file date: 18 ربيع****الثاني, 1430  18:29

Scanning for 1347764 virus strains and unwanted programs.

Licensee        : Avira AntiVir Personal - FREE Antivirus
Serial number   : 0000149996-ADJIE-0000001
Platform        : Windows XP
Windows version : (Service Pack 3)  [5.1.2600]
Boot mode       : Save mode
Username        : Administrator
Computer name   : WINXP-07E684CEF

Version information:
BUILD.DAT       : 9.0.0.387     17962 Bytes  28/03/1430 11:04:00
AVSCAN.EXE      : 9.0.3.3      464641 Bytes  29/02/1430 09:13:26
AVSCAN.DLL      : 9.0.3.0       40705 Bytes  03/03/1430 07:58:24
LUKE.DLL        : 9.0.3.2      209665 Bytes  25/02/1430 08:35:49
LUKERES.DLL     : 9.0.2.0       12033 Bytes  03/03/1430 07:58:52
ANTIVIR0.VDF    : 7.1.0.0    15603712 Bytes  27/10/1429 09:30:36
ANTIVIR1.VDF    : 7.1.2.12    3336192 Bytes  16/02/1430 17:33:26
ANTIVIR2.VDF    : 7.1.3.0     1330176 Bytes  06/04/1430 15:22:55
ANTIVIR3.VDF    : 7.1.3.43     178688 Bytes  18/04/1430 15:22:58
Engineversion   : 8.2.0.138
AEVDF.DLL       : 8.1.1.0      106868 Bytes  01/02/1430 14:36:42
AESCRIPT.DLL    : 8.1.1.73     373114 Bytes  18/04/1430 15:23:19
AESCN.DLL       : 8.1.1.10     127348 Bytes  18/04/1430 15:23:18
AERDL.DLL       : 8.1.1.3      438645 Bytes  29/10/1429 15:24:41
AEPACK.DLL      : 8.1.3.12     397687 Bytes  18/04/1430 15:23:17
AEOFFICE.DLL    : 8.1.0.36     196987 Bytes  02/03/1430 17:01:56
AEHEUR.DLL      : 8.1.0.114   1700214 Bytes  18/04/1430 15:23:14
AEHELP.DLL      : 8.1.2.2      119158 Bytes  02/03/1430 17:01:56
AEGEN.DLL       : 8.1.1.33     340340 Bytes  18/04/1430 15:23:02
AEEMU.DLL       : 8.1.0.9      393588 Bytes  09/10/1429 11:32:40
AECORE.DLL      : 8.1.6.7      176502 Bytes  18/04/1430 15:22:59
AEBB.DLL        : 8.1.0.3       53618 Bytes  09/10/1429 11:32:40
AVWINLL.DLL     : 9.0.0.3       18177 Bytes  14/12/1429 05:47:59
AVPREF.DLL      : 9.0.0.1       43777 Bytes  07/12/1429 07:32:15
AVREP.DLL       : 8.0.0.3      155905 Bytes  24/01/1430 11:34:28
AVREG.DLL       : 9.0.0.0       36609 Bytes  07/12/1429 07:32:09
AVARKT.DLL      : 9.0.0.1      292609 Bytes  14/02/1430 04:52:24
AVEVTLOG.DLL    : 9.0.0.7      167169 Bytes  04/02/1430 07:37:08
SQLITE3.DLL     : 3.6.1.0      326401 Bytes  02/02/1430 12:03:49
SMTPLIB.DLL     : 9.2.0.25      28417 Bytes  07/02/1430 05:21:33
NETNT.DLL       : 9.0.0.0       11521 Bytes  07/12/1429 07:32:10
RCIMAGE.DLL     : 9.0.0.21    2438401 Bytes  14/02/1430 08:45:45
RCTEXT.DLL      : 9.0.35.0      87297 Bytes  15/03/1430 12:55:12

Configuration settings for the scan:
Jobname.............................: Complete system scan
Configuration file..................: c:\program files\avira\antivir desktop\sysscan.avp
Logging.............................: low
Primary action......................: interactive
Secondary action....................: ignore
Scan master boot sector.............: on
Scan boot sector....................: on
Boot sectors........................: C:, D:, E:,
Process scan........................: on
Scan registry.......................: on
Search for rootkits.................: on
Integrity checking of system files..: off
Scan all files......................: All files
Scan archives.......................: on
Recursion depth.....................: 20
Smart extensions....................: on
Macro heuristic.....................: on
File heuristic......................: medium
Deviating risk categories...........: +APPL,+GAME,+JOKE,+PCK,+SPR,

Start of the scan: 18 ربيع****الثاني, 1430  18:29

Starting search for hidden objects.
The driver could not be initialized.

The scan of running processes will be started
Scan process 'avscan.exe' - '1' Module(s) have been scanned
Scan process 'avcenter.exe' - '1' Module(s) have been scanned
Scan process 'explorer.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'lsass.exe' - '1' Module(s) have been scanned
Scan process 'services.exe' - '1' Module(s) have been scanned
Scan process 'winlogon.exe' - '1' Module(s) have been scanned
Scan process 'csrss.exe' - '1' Module(s) have been scanned
Scan process 'smss.exe' - '1' Module(s) have been scanned
11 processes with 11 modules were scanned

Starting master boot sector scan:

Start scanning boot sectors:

Starting to scan executable files (registry).
The registry was scanned ( '54' files ).


Starting the file scan:

Begin scan in 'C:\' <master>
C:\pagefile.sys
    [WARNING]   The file could not be opened!
    [NOTE]      This file is a Windows system file.
    [NOTE]      This file cannot be opened for scanning.
C:\Documents and Settings\Administrator\Desktop\New Folder\ComboFix.exe
  [0] Archive type: RAR SFX (self extracting)
    --> 32788R22FWJFW\psexec.cfexe
      [1] Archive type: RSRC
      --> Object
        [DETECTION] Contains recognition pattern of the APPL/PsExec.E application
C:\Program Files\Common Files\BOONTY Shared\Service\Boonty.exe
    [DETECTION] Contains recognition pattern of the APPL/BoontyGames application
C:\Program Files\SWiSHE.NET\SWiSH2 Book\source\sjc.txt
    [DETECTION] Contains recognition pattern of the JOKE/Rjump joke
Begin scan in 'D:\' <programs>
D:\شرح compo fix\ComboFix.exe
  [0] Archive type: RAR SFX (self extracting)
    --> 32788R22FWJFW\psexec.cfexe
      [1] Archive type: RSRC
      --> Object
        [DETECTION] Contains recognition pattern of the APPL/PsExec.E application
Begin scan in 'E:\' <zhraa>

Beginning disinfection:
C:\Documents and Settings\Administrator\Desktop\New Folder\ComboFix.exe
    [NOTE]      The file was moved to '4a506634.qua'!
C:\Program Files\Common Files\BOONTY Shared\Service\Boonty.exe
    [DETECTION] Contains recognition pattern of the APPL/BoontyGames application
    [NOTE]      The file was moved to '4a526635.qua'!
C:\Program Files\SWiSHE.NET\SWiSH2 Book\source\sjc.txt
    [DETECTION] Contains recognition pattern of the JOKE/Rjump joke
    [NOTE]      The file was moved to '4a466630.qua'!
D:\شرح compo fix\ComboFix.exe
    [NOTE]      The file was moved to '4a506635.qua'!


End of the scan: 18 ربيع****الثاني, 1430  19:18
Used time: 47:03 Minute(s)

The scan has been done completely.

   7157 Scanned directories
 319204 Files were scanned
      4 Viruses and/or unwanted programs were found
      0 Files were classified as suspicious
      0 files were deleted
      0 Viruses and unwanted programs were repaired
      4 Files were moved to quarantine
      0 Files were renamed
      1 Files cannot be scanned
 319199 Files not concerned
   3093 Archives were scanned
      1 Warnings
      5 Notes
كود:
Avira AntiVir Personal
Report file date: 18 ربيع****الثاني, 1430  19:23

Scanning for 1347764 virus strains and unwanted programs.

Licensee        : Avira AntiVir Personal - FREE Antivirus
Serial number   : 0000149996-ADJIE-0000001
Platform        : Windows XP
Windows version : (Service Pack 3)  [5.1.2600]
Boot mode       : Normally booted
Username        : SYSTEM
Computer name   : WINXP-07E684CEF

Version information:
BUILD.DAT       : 9.0.0.387     17962 Bytes  28/03/1430 11:04:00
AVSCAN.EXE      : 9.0.3.3      464641 Bytes  29/02/1430 09:13:26
AVSCAN.DLL      : 9.0.3.0       40705 Bytes  03/03/1430 07:58:24
LUKE.DLL        : 9.0.3.2      209665 Bytes  25/02/1430 08:35:49
LUKERES.DLL     : 9.0.2.0       12033 Bytes  03/03/1430 07:58:52
ANTIVIR0.VDF    : 7.1.0.0    15603712 Bytes  27/10/1429 09:30:36
ANTIVIR1.VDF    : 7.1.2.12    3336192 Bytes  16/02/1430 17:33:26
ANTIVIR2.VDF    : 7.1.3.0     1330176 Bytes  06/04/1430 15:22:55
ANTIVIR3.VDF    : 7.1.3.43     178688 Bytes  18/04/1430 15:22:58
Engineversion   : 8.2.0.138
AEVDF.DLL       : 8.1.1.0      106868 Bytes  01/02/1430 14:36:42
AESCRIPT.DLL    : 8.1.1.73     373114 Bytes  18/04/1430 15:23:19
AESCN.DLL       : 8.1.1.10     127348 Bytes  18/04/1430 15:23:18
AERDL.DLL       : 8.1.1.3      438645 Bytes  29/10/1429 15:24:41
AEPACK.DLL      : 8.1.3.12     397687 Bytes  18/04/1430 15:23:17
AEOFFICE.DLL    : 8.1.0.36     196987 Bytes  02/03/1430 17:01:56
AEHEUR.DLL      : 8.1.0.114   1700214 Bytes  18/04/1430 15:23:14
AEHELP.DLL      : 8.1.2.2      119158 Bytes  02/03/1430 17:01:56
AEGEN.DLL       : 8.1.1.33     340340 Bytes  18/04/1430 15:23:02
AEEMU.DLL       : 8.1.0.9      393588 Bytes  09/10/1429 11:32:40
AECORE.DLL      : 8.1.6.7      176502 Bytes  18/04/1430 15:22:59
AEBB.DLL        : 8.1.0.3       53618 Bytes  09/10/1429 11:32:40
AVWINLL.DLL     : 9.0.0.3       18177 Bytes  14/12/1429 05:47:59
AVPREF.DLL      : 9.0.0.1       43777 Bytes  07/12/1429 07:32:15
AVREP.DLL       : 8.0.0.3      155905 Bytes  24/01/1430 11:34:28
AVREG.DLL       : 9.0.0.0       36609 Bytes  07/12/1429 07:32:09
AVARKT.DLL      : 9.0.0.1      292609 Bytes  14/02/1430 04:52:24
AVEVTLOG.DLL    : 9.0.0.7      167169 Bytes  04/02/1430 07:37:08
SQLITE3.DLL     : 3.6.1.0      326401 Bytes  02/02/1430 12:03:49
SMTPLIB.DLL     : 9.2.0.25      28417 Bytes  07/02/1430 05:21:33
NETNT.DLL       : 9.0.0.0       11521 Bytes  07/12/1429 07:32:10
RCIMAGE.DLL     : 9.0.0.21    2438401 Bytes  14/02/1430 08:45:45
RCTEXT.DLL      : 9.0.35.0      87297 Bytes  15/03/1430 12:55:12

Configuration settings for the scan:
Jobname.............................: Complete system scan
Configuration file..................: c:\program files\avira\antivir desktop\sysscan.avp
Logging.............................: low
Primary action......................: interactive
Secondary action....................: ignore
Scan master boot sector.............: on
Scan boot sector....................: on
Boot sectors........................: C:, D:, E:,
Process scan........................: on
Scan registry.......................: on
Search for rootkits.................: on
Integrity checking of system files..: off
Scan all files......................: All files
Scan archives.......................: on
Recursion depth.....................: 20
Smart extensions....................: on
Macro heuristic.....................: on
File heuristic......................: medium
Deviating risk categories...........: +APPL,+GAME,+JOKE,+PCK,+SPR,

Start of the scan: 18 ربيع****الثاني, 1430  19:23

Starting search for hidden objects.
'47047' objects were checked, '0' hidden objects were found.

The scan of running processes will be started
Scan process 'avscan.exe' - '1' Module(s) have been scanned
Scan process 'wuauclt.exe' - '1' Module(s) have been scanned
Scan process 'firefox.exe' - '1' Module(s) have been scanned
Scan process 'IEMonitor.exe' - '1' Module(s) have been scanned
Scan process 'alg.exe' - '1' Module(s) have been scanned
Scan process 'YahooAUService.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'MDM.EXE' - '1' Module(s) have been scanned
Scan process 'AppleMobileDeviceService.exe' - '1' Module(s) have been scanned
Scan process 'avguard.exe' - '1' Module(s) have been scanned
Scan process 'ctfmon.exe' - '1' Module(s) have been scanned
Scan process 'IDMan.exe' - '1' Module(s) have been scanned
Scan process 'avgnt.exe' - '1' Module(s) have been scanned
Scan process 'realsched.exe' - '1' Module(s) have been scanned
Scan process 'UnlockerAssistant.exe' - '1' Module(s) have been scanned
Scan process 'reader_sl.exe' - '1' Module(s) have been scanned
Scan process 'explorer.exe' - '1' Module(s) have been scanned
Scan process 'GoogleUpdate.exe' - '1' Module(s) have been scanned
Scan process 'sched.exe' - '1' Module(s) have been scanned
Scan process 'spoolsv.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'svchost.exe' - '1' Module(s) have been scanned
Scan process 'lsass.exe' - '1' Module(s) have been scanned
Scan process 'services.exe' - '1' Module(s) have been scanned
Scan process 'winlogon.exe' - '1' Module(s) have been scanned
Scan process 'csrss.exe' - '1' Module(s) have been scanned
Scan process 'smss.exe' - '1' Module(s) have been scanned
32 processes with 32 modules were scanned

Starting master boot sector scan:

Start scanning boot sectors:

Starting to scan executable files (registry).
The registry was scanned ( '56' files ).


Starting the file scan:

Begin scan in 'C:\' <master>
C:\pagefile.sys
    [WARNING]   The file could not be opened!
    [NOTE]      This file is a Windows system file.
    [NOTE]      This file cannot be opened for scanning.
C:\System Volume Information\_restore{2FCFF432-6BE0-475C-BE2F-5E9914F3CB75}\RP165\A0045583.exe
  [0] Archive type: RAR SFX (self extracting)
    --> 32788R22FWJFW\psexec.cfexe
      [1] Archive type: RSRC
      --> Object
        [DETECTION] Contains recognition pattern of the APPL/PsExec.E application
C:\System Volume Information\_restore{2FCFF432-6BE0-475C-BE2F-5E9914F3CB75}\RP165\A0045584.exe
    [DETECTION] Contains recognition pattern of the APPL/BoontyGames application
Begin scan in 'D:\' <programs>
D:\System Volume Information\_restore{2FCFF432-6BE0-475C-BE2F-5E9914F3CB75}\RP165\A0045585.exe
  [0] Archive type: RAR SFX (self extracting)
    --> 32788R22FWJFW\psexec.cfexe
      [1] Archive type: RSRC
      --> Object
        [DETECTION] Contains recognition pattern of the APPL/PsExec.E application
Begin scan in 'E:\' <zhraa>

Beginning disinfection:
C:\System Volume Information\_restore{2FCFF432-6BE0-475C-BE2F-5E9914F3CB75}\RP165\A0045583.exe
    [NOTE]      The file was moved to '4a136e72.qua'!
C:\System Volume Information\_restore{2FCFF432-6BE0-475C-BE2F-5E9914F3CB75}\RP165\A0045584.exe
    [DETECTION] Contains recognition pattern of the APPL/BoontyGames application
    [NOTE]      The file was moved to '4b682c9b.qua'!
D:\System Volume Information\_restore{2FCFF432-6BE0-475C-BE2F-5E9914F3CB75}\RP165\A0045585.exe
    [NOTE]      The file was moved to '4b6b45e3.qua'!


End of the scan: 18 ربيع****الثاني, 1430  19:54
Used time: 26:25 Minute(s)

The scan has been done completely.

   7245 Scanned directories
 320506 Files were scanned
      3 Viruses and/or unwanted programs were found
      0 Files were classified as suspicious
      0 files were deleted
      0 Viruses and unwanted programs were repaired
      3 Files were moved to quarantine
      0 Files were renamed
      1 Files cannot be scanned
 320502 Files not concerned
   3095 Archives were scanned
      1 Warnings
      4 Notes
  47047 Objects were scanned with rootkit scan
      0 Hidden objects were found
التوقيع
|
||||
|
13-04-2009, 18:00
|
#19 | ||||
|
التوقيع
|
||||
|
13-04-2009, 18:05
|
#20 | ||||
|
التوقيع
|
||||
|
| أدوات الموضوع | |
| انواع عرض الموضوع | |
|
|
 دنيا الأمل
 مدونة الأمل
 مكتبة الأمل للبرامج
 الخلاصات RSS
 راسلنا
 إرشادات



 لحذف كل ماهو (file missing)


 العرض العادي


